
An access control list in networking is a set of ordered rules that a router, switch or firewall uses to decide which packets to allow and which to drop. ACLs are one of the most basic security tools in any network, and they also help select traffic for features such as NAT, VPNs and quality of service.
This guide explains how ACLs work, how routers process them, wildcard masks, where to apply them and the rules that prevent common mistakes.
Why use ACLs?
- Security: block traffic from untrusted networks or to sensitive servers.
- Traffic control: stop unwanted protocols, such as Telnet, crossing the network.
- Management protection: allow SSH to network devices only from admin subnets.
- Feature selection: define which traffic NAT translates or which traffic a VPN protects.
- Basic performance control: limit bandwidth-heavy traffic at certain points.
How an ACL processes a packet
- The router compares the packet with the first line of the ACL.
- If the line matches, the router applies its action, permit or deny, and stops checking.
- If the line does not match, the router moves to the next line.
- If no line matches, an invisible implicit deny at the end drops the packet.
Because the first match wins, the order of lines matters. Place specific rules before general ones.
Inbound vs outbound ACLs
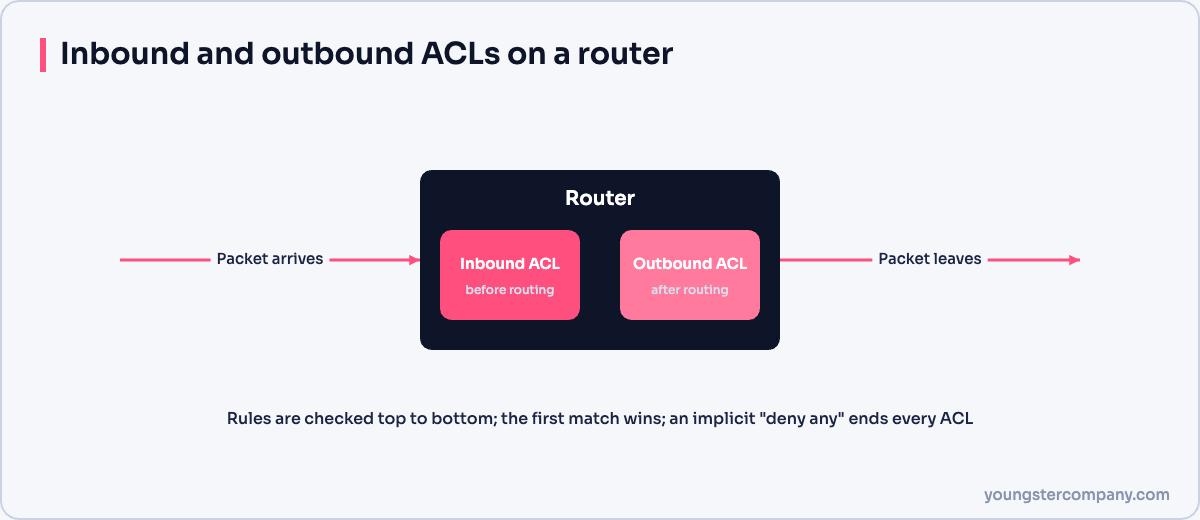
- An inbound ACL checks packets as they arrive on an interface, before routing. It saves resources, because the router drops unwanted packets early.
- An outbound ACL checks packets after routing, as they leave an interface.
You can apply one ACL per interface, per direction and per protocol (IPv4 or IPv6).
Wildcard masks
ACLs use wildcard masks instead of subnet masks. A 0 bit means “must match”, and a 1 bit means “ignore”.
| To match | Address | Wildcard mask |
|---|---|---|
| One host | 192.168.1.10 | 0.0.0.0 (or use host 192.168.1.10) |
| A /24 subnet | 192.168.1.0 | 0.0.0.255 |
| A /16 network | 172.16.0.0 | 0.0.255.255 |
| Everything | 0.0.0.0 | 255.255.255.255 (or use any) |
A quick trick: subtract the subnet mask from 255.255.255.255. For example, 255.255.255.255 minus 255.255.255.0 gives 0.0.0.255.
Creating and applying an ACL
ip access-list extended PROTECT-SERVERS
 permit tcp 10.10.0.0 0.0.255.255 host 10.1.1.20 eq 443
 deny   ip any host 10.1.1.20 log
 permit ip any any
!
interface GigabitEthernet0/1
 ip access-group PROTECT-SERVERS in
This example lets the 10.10.0.0/16 network reach a web server on HTTPS only. It then logs and blocks everything else to that server, while other traffic passes normally.
Basic rules for ACLs
- Write the ACL in a text editor first, and review it before you apply it.
- Put the most specific statements at the top.
- Remember the implicit deny; add a final permit if other traffic must pass.
- Place extended ACLs near the source and standard ACLs near the destination.
- Use named ACLs and remarks, so others understand the purpose.
- Avoid editing an ACL on a live interface without a rollback plan.
- Test on a lab or during a maintenance window when possible.
Verify and troubleshoot
| Command | What it shows |
|---|---|
show access-lists | Every line, with hit counters |
show ip interface Gi0/1 | Which ACLs apply, and in which direction |
clear access-list counters | Resets counters before a test |
If traffic is blocked unexpectedly, check the hit counters and the order of lines first.
Related guides
Sources
Need help with network security? We test routers, firewalls, ACLs and segmentation as part of our VAPT services and hardening audits. Contact us for a quote.


Pingback: Types of ACLs in Networking - Youngster Company