OSPF (Open Shortest Path First) is the most widely used interior routing protocol in enterprise networks. It is an open standard, so routers from Cisco, Juniper, Arista, MikroTik and others can all run it together. OSPF builds a complete map of the network and then calculates the shortest path to every destination.
This guide explains how OSPF works, its key terms, areas, cost and a basic configuration with verification commands.
OSPF at a glance
| Feature | Value |
|---|---|
| Type | Link-state interior gateway protocol |
| Standard | OSPFv2 for IPv4 (RFC 2328), OSPFv3 for IPv6 (RFC 5340) |
| Algorithm | Dijkstra’s shortest path first (SPF) |
| Metric | Cost, based on interface bandwidth |
| Administrative distance | 110 on Cisco |
| Transport | IP protocol 89 |
| Multicast addresses | 224.0.0.5 (all OSPF routers), 224.0.0.6 (DR and BDR) |
How OSPF works
- Discover neighbours: routers send hello packets on OSPF-enabled interfaces.
- Form adjacencies: compatible neighbours exchange their link-state databases.
- Flood link-state advertisements (LSAs): every router learns about every link in its area.
- Run SPF: each router calculates the shortest path tree from itself to all destinations.
- Install routes: the best paths go into the routing table.
- React to change: when a link fails, routers flood new LSAs and recalculate.
Hello packets
Hello packets discover neighbours and confirm they are still alive. By default, on broadcast networks such as Ethernet, routers send hellos every 10 seconds and declare a neighbour down after 40 seconds. Neighbours must agree on several values, including:
- area ID;
- subnet and mask;
- hello and dead intervals;
- authentication settings;
- area type, such as stub.
If these do not match, routers will not become neighbours. In practice, mismatched timers or areas cause many OSPF problems.
Neighbour states
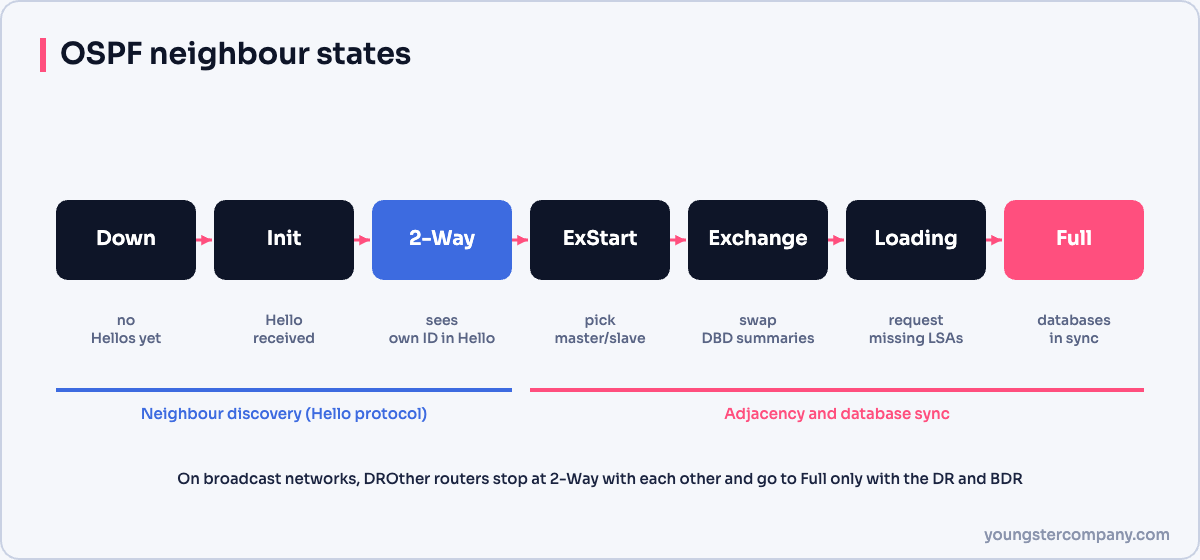
Routers move through states: Down, Init, 2-Way, ExStart, Exchange, Loading and finally Full. A FULL state means the routers have synchronised databases. On Ethernet, routers that are neither DR nor BDR stay at 2-WAY with each other, and that is normal.
Key OSPF terms
- Router ID: a unique 32-bit ID, usually set manually with
router-id. - Link-state database (LSDB): the map of the network, identical on all routers in an area.
- DR and BDR: on multi-access networks, a designated router and a backup reduce flooding.
- Cost: the metric. On Cisco, cost equals the reference bandwidth (100 Mbps by default) divided by the interface bandwidth.
OSPF areas
Large networks split into areas to limit flooding and SPF calculations. Every multi-area design has a backbone, area 0, and all other areas connect to it.
- Internal routers have all interfaces in one area.
- Area border routers (ABRs) connect an area to area 0.
- Autonomous system boundary routers (ASBRs) bring in routes from outside, such as BGP or static routes.
Special area types, such as stub and NSSA, reduce the routes an area must carry.
Basic single-area configuration
router ospf 1
 router-id 1.1.1.1
 auto-cost reference-bandwidth 100000
 passive-interface default
 no passive-interface GigabitEthernet0/0
 network 10.0.12.0 0.0.0.255 area 0
 network 192.168.1.0 0.0.0.255 area 0
Alternatively, enable OSPF directly on an interface:
interface GigabitEthernet0/0
 ip ospf 1 area 0
The higher reference bandwidth gives fast links different costs. Meanwhile, passive-interface default stops hellos on user-facing ports, which improves security.
Verification commands
show ip ospf neighbor
show ip ospf interface brief
show ip route ospf
show ip ospf database
Best practices
- Set router IDs manually.
- Use authentication, such as HMAC-SHA, between neighbours.
- Make user-facing interfaces passive.
- Keep area 0 contiguous and design areas around natural boundaries.
- Use the same reference bandwidth on every router.
Related guides
Sources
Need help with network security? We test routers, firewalls, ACLs and segmentation as part of our VAPT services and hardening audits. Contact us for a quote.