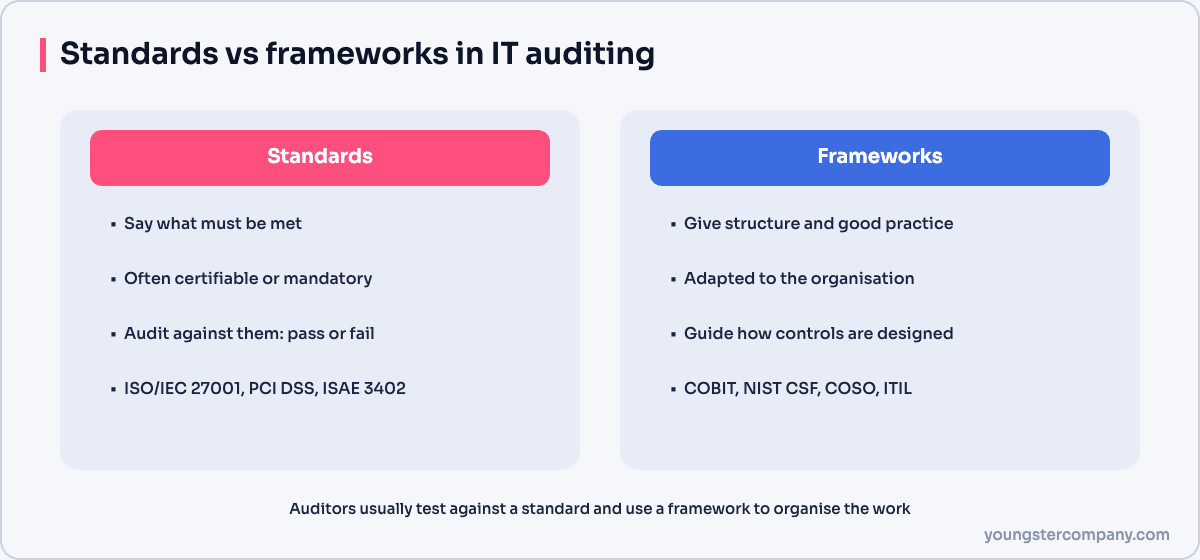
IT auditors need two kinds of reference. Auditing standards describe how to perform an audit professionally. Control frameworks describe what good control looks like, so auditors have criteria to test against. Knowing which IT auditing standards and frameworks apply makes audits consistent and credible.
This guide explains the most widely used ones and when each fits.
Auditing standards: how to audit
| Standard | Publisher | Use |
|---|---|---|
| ITAF (IT Assurance Framework) | ISACA | Professional standards for IT audit and assurance, used by CISA holders |
| Global Internal Audit Standards | The Institute of Internal Auditors (IIA) | Standards for internal audit functions, effective from January 2025 |
| ISO 19011 | ISO | Guidelines for auditing management systems |
| ISO/IEC 27007 | ISO/IEC | Guidance for auditing an ISMS |
| ISAE 3402 and SSAE 18 | IAASB and AICPA | Assurance reports on service organizations’ controls |
Together, these standards cover independence, planning, evidence, documentation, reporting and quality.
Control frameworks: what to audit against
COBIT
COBIT, from ISACA, is a framework for governance and management of enterprise IT. Its current version, COBIT 2019, defines governance and management objectives, such as managing security, changes and operations. As a result, auditors use it to assess IT governance and processes.
ISO/IEC 27001 and 27002
This pair is the most widely recognised security standard. The first sets requirements for an information security management system, and its Annex A lists 93 controls. Its companion, 27002, then explains each control in detail. Read our ISO 27001 Annex A guide.
NIST Cybersecurity Framework 2.0
The NIST CSF organises security outcomes into six functions: Govern, Identify, Protect, Detect, Respond and Recover. It is popular for maturity assessments and board reporting.
NIST SP 800-53
In contrast, this catalogue contains hundreds of detailed security and privacy controls in families such as access control, audit and accountability, incident response and system integrity. US federal agencies must use it, and many others use it as a reference.
SOC 2
SOC 2 reports, issued under AICPA standards, evaluate a service organization against the Trust Services Criteria: security, availability, processing integrity, confidentiality and privacy. A Type II report tests controls over a period, typically six to twelve months.
PCI DSS
The Payment Card Industry Data Security Standard applies to anyone who stores, processes or transmits card data. Version 4.0.1 is current, and its future-dated requirements became mandatory in March 2025.
COSO
COSO’s Internal Control framework underpins financial controls and is widely used for internal financial controls reporting. IT general controls support it.
ITIL
ITIL 4 describes good practice for IT service management, such as incident, change and problem management. Auditors use it as a benchmark for operational processes.
CIS Controls
The CIS Critical Security Controls offer a prioritised, practical list of 18 safeguard areas, which suits smaller organizations.
Choosing the right criteria
- Certification or customer demand: ISO/IEC 27001 or SOC 2.
- Card payments: PCI DSS.
- IT governance review: COBIT.
- Maturity assessment and board reporting: NIST CSF.
- Detailed technical control testing: NIST SP 800-53 or CIS Controls.
- Indian regulated sectors: the relevant RBI, SEBI or IRDAI guidelines, often mapped to ISO 27001.
In practice, many organizations map one set of controls to several frameworks, so one test serves several audits.
Related guides
Sources
Preparing for an ISO 27001 or IT audit? Our ISO 27001 readiness assessment finds your gaps before the auditor does. You can also start with our free ISO 27001:2022 readiness checklist, or contact us for a quote.